How IT security goes hand in hand with hackers.
The walls are virtual, the risks real. EOS is improving its data security using “penetration tests”, where hackers attack the company under real-life conditions.
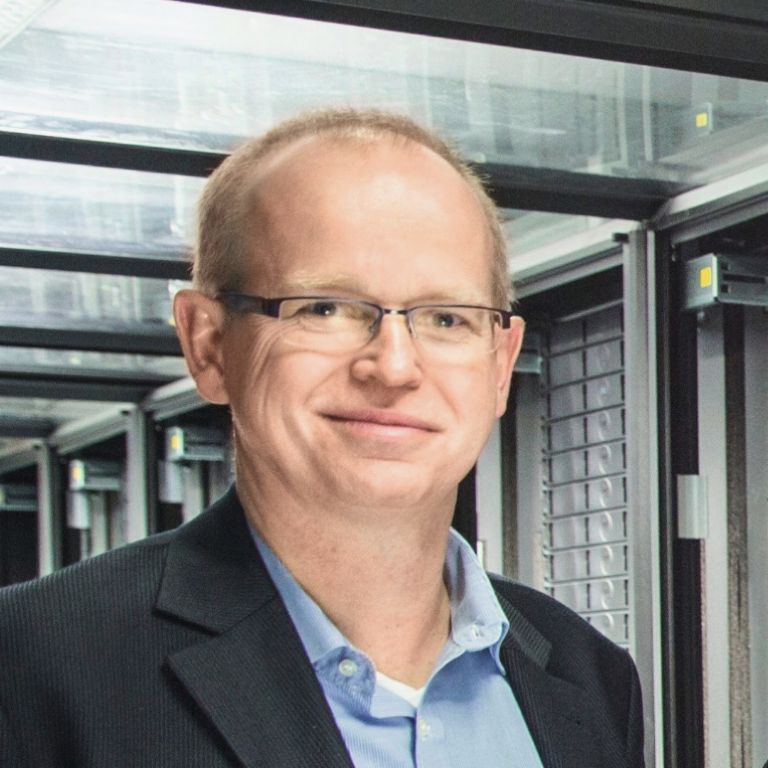
If you talk to Gunnar Woitack about how companies like the EOS Group protect themselves from hacker attacks, then sooner or later the topic of the Brothers Grimm comes up. “It’s like a race between the hare and the hedgehog,” says the IT security expert. “We put up fences to keep attackers out and the hackers constantly develop new techniques for breaking them down.”
Since January 2015, Gunnar Woitack has been in charge of IT security across the EOS Group. As Chief Information Security Officer (CISO) at EOS Technology Solutions, he is something like the “keeper of the crown jewels” for the entire Group. Whereas companies like VW, for example, never let their vehicle technology patents out of their sight, the most valuable assets at EOS include above all the data of defaulting payers.
In addition – like virtually all companies – EOS stores data about its customers and other stakeholders on its servers. For EOS, handling this information responsibly in-house, and protecting it from attacks and misuse from outside, are top priorities. After all, this security is the basis for the trust placed in EOS.
Hacker attack provides information on IT security.
To ensure the greatest possible degree of data security at the more than 60 EOS companies in 26 countries, Woitack regularly engages professionals – specialised hackers who scan the virtual walls of EOS for security loopholes. This year too, these “white hat” hackers – as they are known – will carry out what is known as a black box penetration test. In the process, the external partner receives several hundred EOS IP addresses. “This kind of test takes several hours,” Woitack says. “And a lot of it is automated.”
There is no such thing as 100% security for companies.
In addition, EOS also periodically arranges for what are known as grey and white box tests. These cyber-attacks “let more light into the box”, i.e. the hackers also receive access data and/or the source code of web applications. To use the analogy of the hacker as a burglar, they either get the key to the house or even the room layouts and alarm system details. Despite these very thorough penetration tests, EOS is nevertheless not lulled into a false sense of security, stresses Woitack. Because ultimately, nobody is completely protected from an attack.
There is no 100% security. Even the CIA and FBI get hacked.
Hacker attack shows that the error rate is going down.
Basically, the EOS systems associated with the internet have become more and more secure over the years. The error rate in the penetration tests is declining, and awareness of data security among the workforce is constantly increasing, Woitack says. “The recurring tests steer the focus in the right direction.”
And there’s one thing that the IT security expert is sure of: even in ten years, simulated hacker attacks will still be an effective means of exposing vulnerabilities in a company’s IT security. Because the race between the hare and the hedgehog continues. “But we are working very hard on dealing with it,” says Woitack. “We take the risks very seriously and naturally are also investing a lot of money in security.”
Photo Credits: Sebastian Vollmert / EOS, Hack Capital / Unsplash
Explora más de EOS